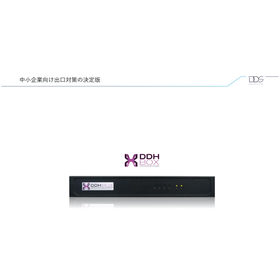
A solution for automatically detecting and blocking unauthorized communications to prevent information leaks!
DDHBOX is an exit strategy solution designed to prevent information leaks caused by cyber attacks. It addresses new types of malware that existing UTM and antivirus solutions cannot fully protect against, automatically detecting, blocking, and notifying about unauthorized communications. ■ Automatic detection and blocking of unauthorized communications It detects unauthorized communications originating from infected devices in real-time and automatically blocks them, reducing the risk of information leaks. ■ Support for new attacks Utilizing threat information from JSOC, one of the largest security monitoring centers in Japan, it updates the latest C2 server list daily, ensuring constant readiness against the latest threats. ■ Easy to implement It can be used simply by installing it on existing networks. Companies without dedicated security personnel can operate it with confidence. ■ Support even after an incident occurs With support systems for data leak investigations, data recovery, and consulting, rapid response is possible in the event of an emergency. This is a recommended security solution for companies that want to protect their information assets and strengthen their cyber attack countermeasures.
Inquire About This Product
basic information
DDHBOX is a security appliance for outbound measures that automatically detects, blocks, and notifies about unauthorized communications. - Countermeasure method: Outbound measures (detection and blocking of unauthorized communications) - Detection targets: Unauthorized communications from existing malware and new types of malware - Functions: Detection of unauthorized communications, automatic blocking, notifications, communication monitoring - Blacklist: Reflects threat information from JSOC, one of the largest security monitoring centers in Japan - Threat information updates: Automatically updated every day, 365 days a year - Compatible environment: Can be installed in existing networks - Interface: RJ45 1GbE 4 ports, USB3.0×2, HDMI×1, console port - CPU: Intel Celeron Processor N3160 - Memory: 4GB DDR3 1600MHz - Storage: SATA-DOM MLC 16GB - Operational support: Data leakage investigation during incidents, data recovery, consulting support - Additional services: Cyber insurance (up to 3 million yen) It addresses the risk of information leakage that cannot be prevented by firewalls, UTM, antivirus, and EDR, thereby strengthening corporate security measures.
Price range
Delivery Time
Applications/Examples of results
For case studies and implementation effects of this product, please watch the archived webinar. ▶ Watch the archived webinar here URL: https://sandx.seminarone.com/1AGlmdvxpUm20xpreFvraA/event *The content is the same as the archived webinar above.
catalog(1)
Download All Catalogs
Company information

We are a trading company that has been supporting manufacturing in the IoT era for 70 years. Our domestic locations include our headquarters in Kyoto (Minami-ku, Kyoto City), a sales office in Nagoya (Meito-ku, Nagoya City), a sales office in Shiga (Ritto City, Shiga Prefecture), a branch office in Akashi (Kakogun, Hyogo Prefecture), and a sales office in Okayama (Kita-ku, Okayama City), as well as two overseas locations in Malaysia and the Philippines.